

The rapid advances of quantum computing have become a key concern for the crypto community a while ago. Now there's another vulnerability to take into account.
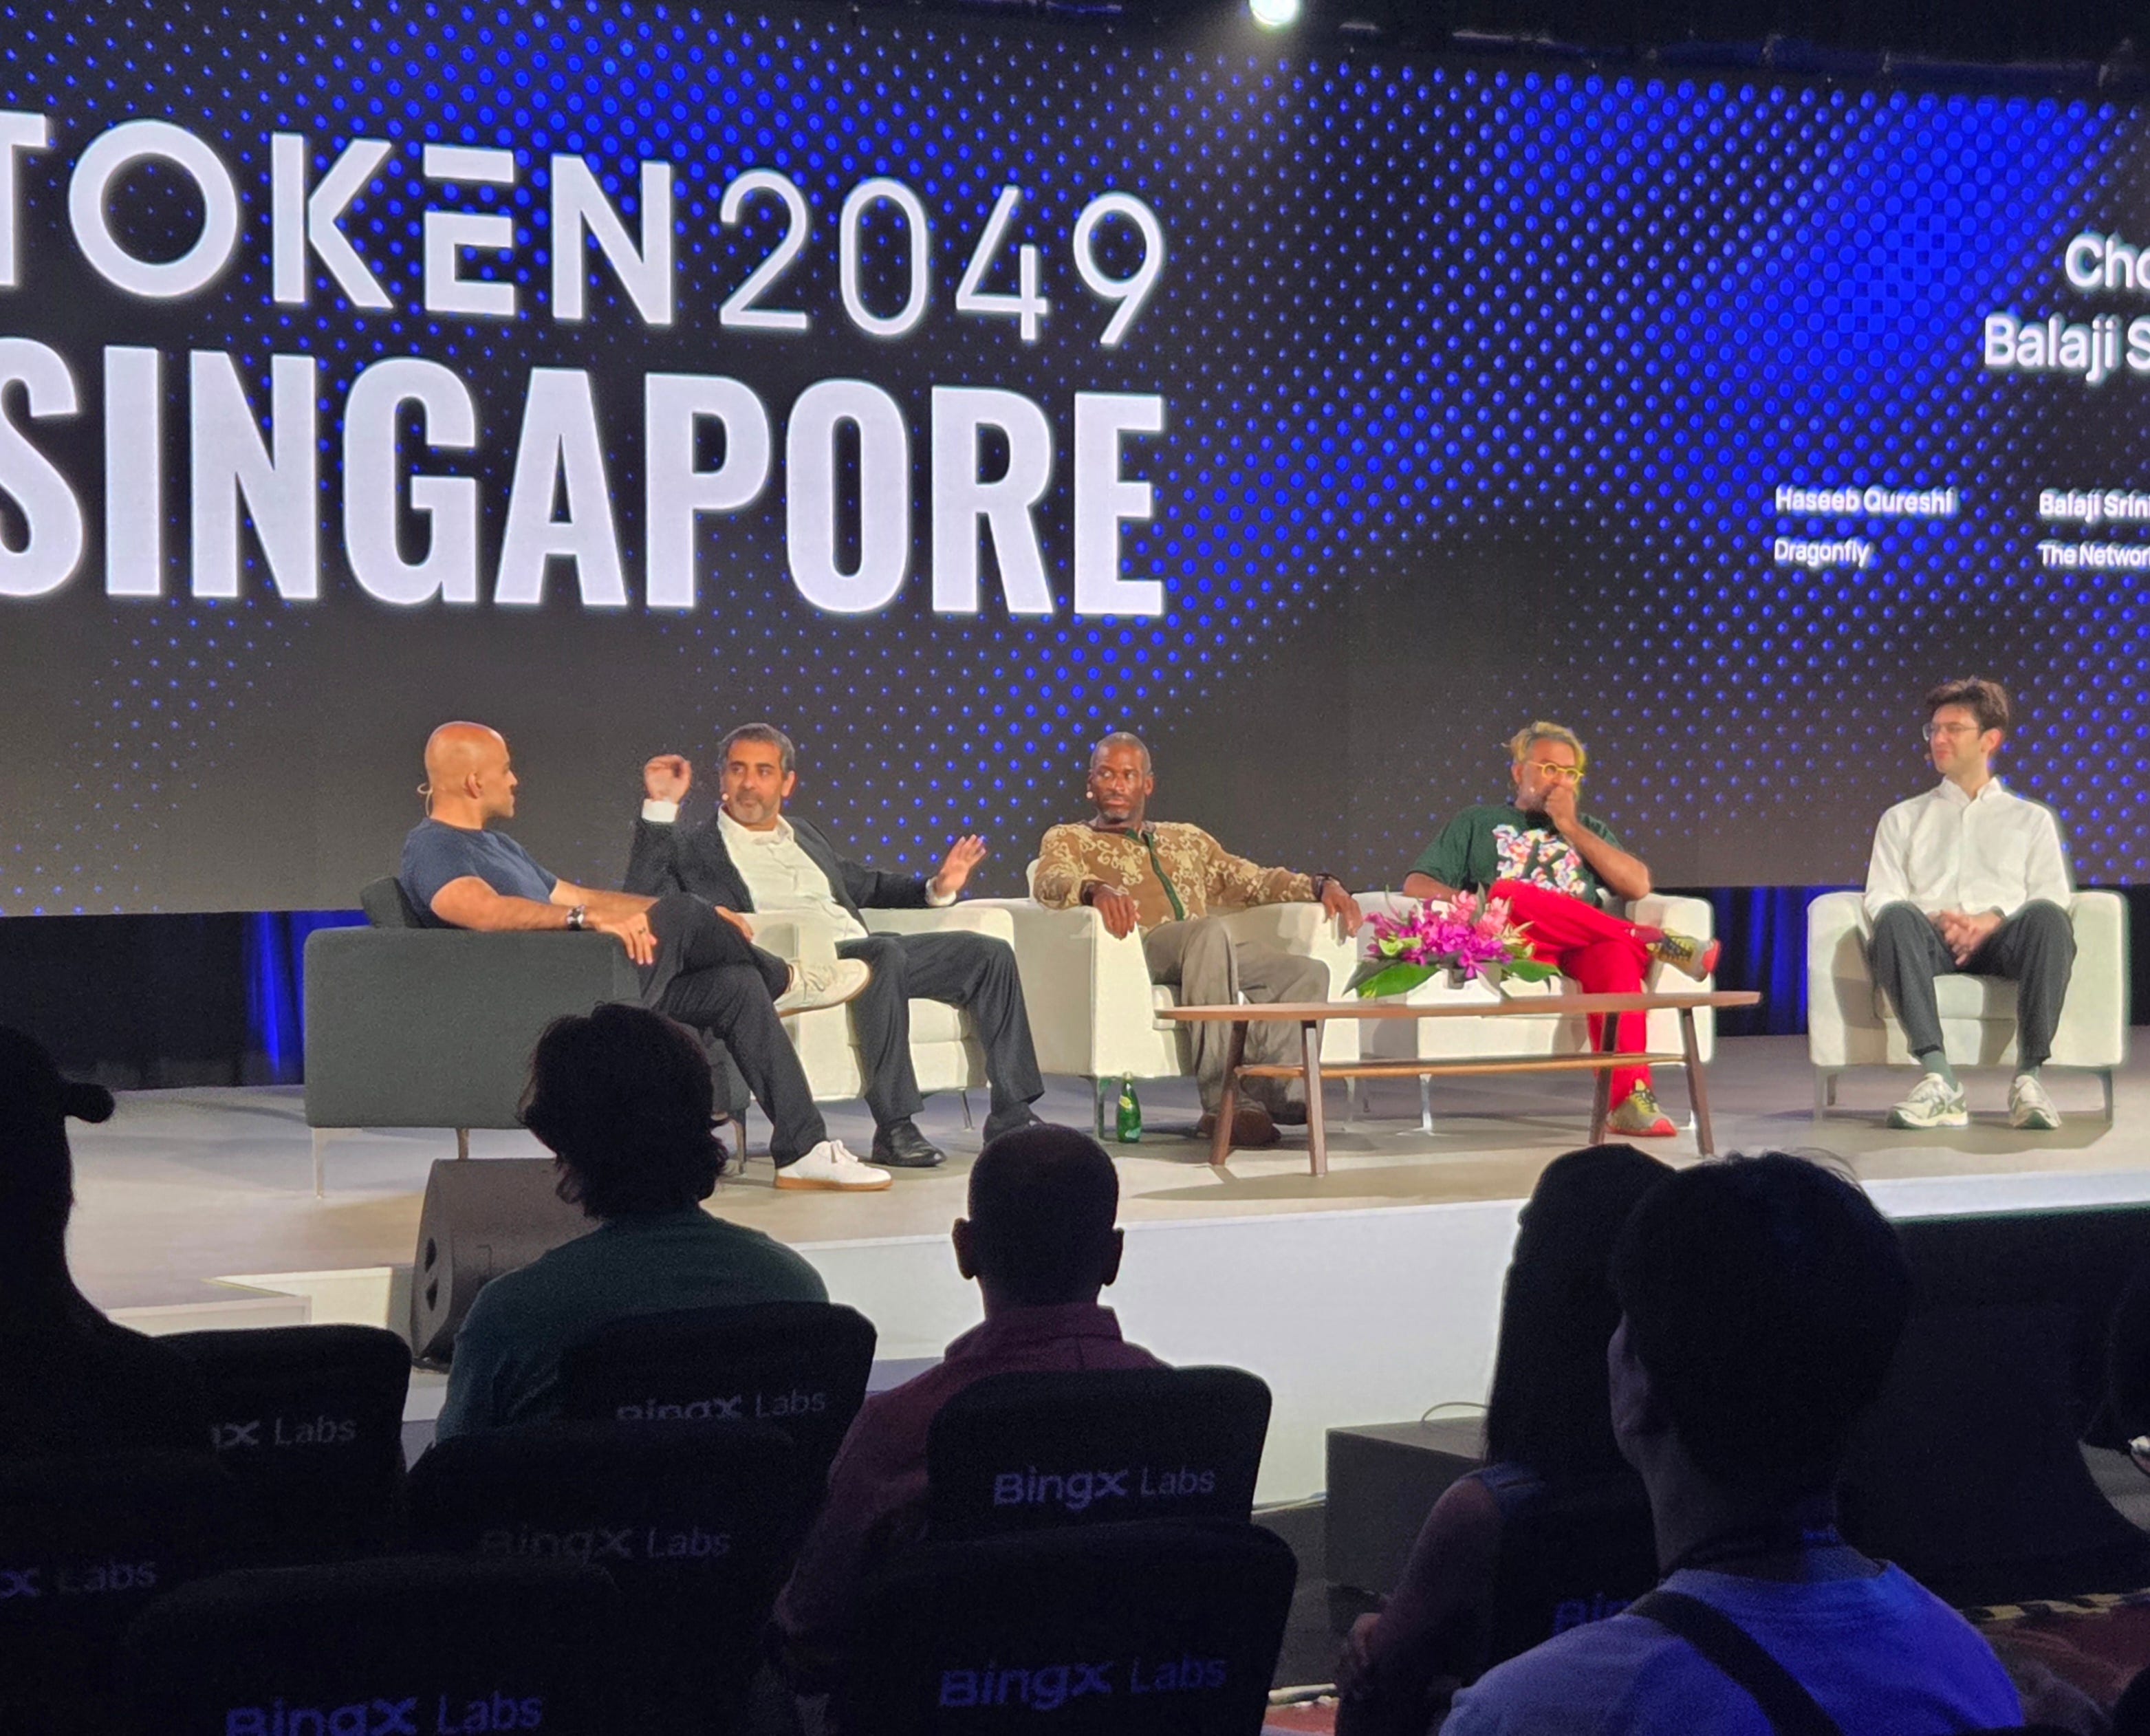
Just as the industry gathered in Singapore for Token2049, its biggest event globally, AI frontier lab OpenAI published solutions to over 700 foundational math problems, spending just 3 hours of compute for each. Mathematicians were left in shock, and cryptographers raised their eyebrows.
Cryptography wasn't mentioned at all in the OpenAI release, an omission that Dragonfly VC Haseeb Qureshi called “weird.” One explanation could be export restrictions for this sensitive cryptographic research, which prohibit the labs from publishing certain findings. Or, as Qureshi speculated on stage, OpenAI could have found something alarming, such as the ability to break elliptic curve cryptography, and is right now working behind closed doors with the government on how to address it.
The mechanism that protects crypto
ECDSA, the elliptic curve digital signature algorithm in question, is a form of public key cryptography that generates and verifies signatures for secure transactions. It is used well beyond cryptocurrencies. Financial institutions rely on it, alongside other algorithms like RSA, to verify and secure mobile banking traffic.
Across the internet, Transport Layer Security (TLS) and Secure Shell (SSH) rely on ECDSA to authenticate connections. As frontier AI keeps advancing, standards organizations and industry bodies are already racing to migrate these protocols to post-quantum algorithms.
In the decentralized crypto space, developers are already on high alert, particularly after Google published an explosive paper on the progress of quantum science in March. Engineering teams are now exploring solutions that upgrade signature schemes, enabling crypto holders to move their funds to post-quantum wallets, while drafting contingency plans for when “Q-Day” inevitably arrives.
The hunt for Satoshi’s stash
Bitcoin, the most established and distributed network, is notoriously slow to execute protocol upgrades, raising concerns among investors whether it can adapt on time. There is also the question of what happens to the about 1.1 million of Satoshi’s coins that haven't moved since the bitcoin founder disappeared at the end of 2010.
Early coins are stored in so-called Pay-to-Public-Key addresses that expose the public keys directly on the blockchain. A quantum computer running Shor’s algorithm can reverse-engineer the private keys from the public keys, drain the funds, and probably crash the bitcoin price overnight.
As few realistically expect Satoshi to return or for those funds to be moved to safety, the community has begun debating how to avoid a potential catastrophe. One option would be freezing the addresses which would require a protocol upgrade and soft fork that needs consensus of the node operators. In the worst case scenario, it could trigger a chain split. However, previous successful upgrades like Segwit and Taproot demonstrate that these changes can work out just fine.
Freezing funds could also alienate bitcoin purists who view such an intervention as an attack on property rights and would likely oppose the soft fork. Satoshi’s funds would effectively become a massive bounty for quantum scientists racing to crack the algorithm first and cash the prize. It left some people wondering if the US government, leveraging its vast compute power, should try to get the coins first to prevent them from falling in the hands of a rogue state actor.
Shutting down the crypto doomers
Justin Drake, the Ethereum Foundation researcher who sparked the current debate, argues that ECDSA could fall well before Q-Day, “in the worst case in months not years.” He recommended entering “bunker mode,” urging holders to move funds to addresses that have never signed a transaction, thereby keeping their public keys hidden behind a cryptographic hash. Hash functions like SHA-256, a fundamental pillar of cryptocurrencies, remain virtually unbreakable, by AI and quantum computers alike.
Qureshi dismissed this as cryptographic doomerism, comparing the rush to bunker mode to buying canned food in preparation for a nuclear winter. Still he thinks that the broader ecosystem, including developers, wallet providers, exchanges and end users, should mobilize and devise a strategy that it will adopt in a worst-case scenario. Users could for example generate a hash-based ZK-proof (for zero-knowledge proof) of their seed phrase to transition their assets to a new address.
A cryptographic hash acts as a one-way mathematical function that compresses data into a unique fixed-size output. A ZK-proof builds on this, proving that a statement is true without revealing the underlying data. Modern ZK systems use hashes as their primary building blocks.
Eli Ben-Sasson of StarkWare, the team behind the Ethereum layer 2 Starknet, has been a pioneer advocating for ZK-proofs in the blockchain world. As co-inventor of STARKs, he helped create the mathematical breakthroughs that made proof verification faster and therefore more practical. In the light of the current events, Ben-Sasson advocated in Singapore for greater “crypto agility,” urging the industry to move faster in replacing vulnerable algorithms, particularly by using hash-based STARK signatures.
The recent progress of AI-accelerated math is another reason, along with quantum, why ECDSA might fall faster than expected, Ethereum founder Vitalik Buterin weighed in. He believes that even lattices, widely viewed as a leading quantum-resistant approach, could take serious hits from AI math in the coming years.
“For signatures and proofs, we already know how to go hash-only,” he wrote. For Buterin, the bigger challenge is the wider public-key encryption that goes far beyond blockchains. “Secure communication, anonymizing protocols, lots of things need public-key encryption.”